Services
Security Engineering
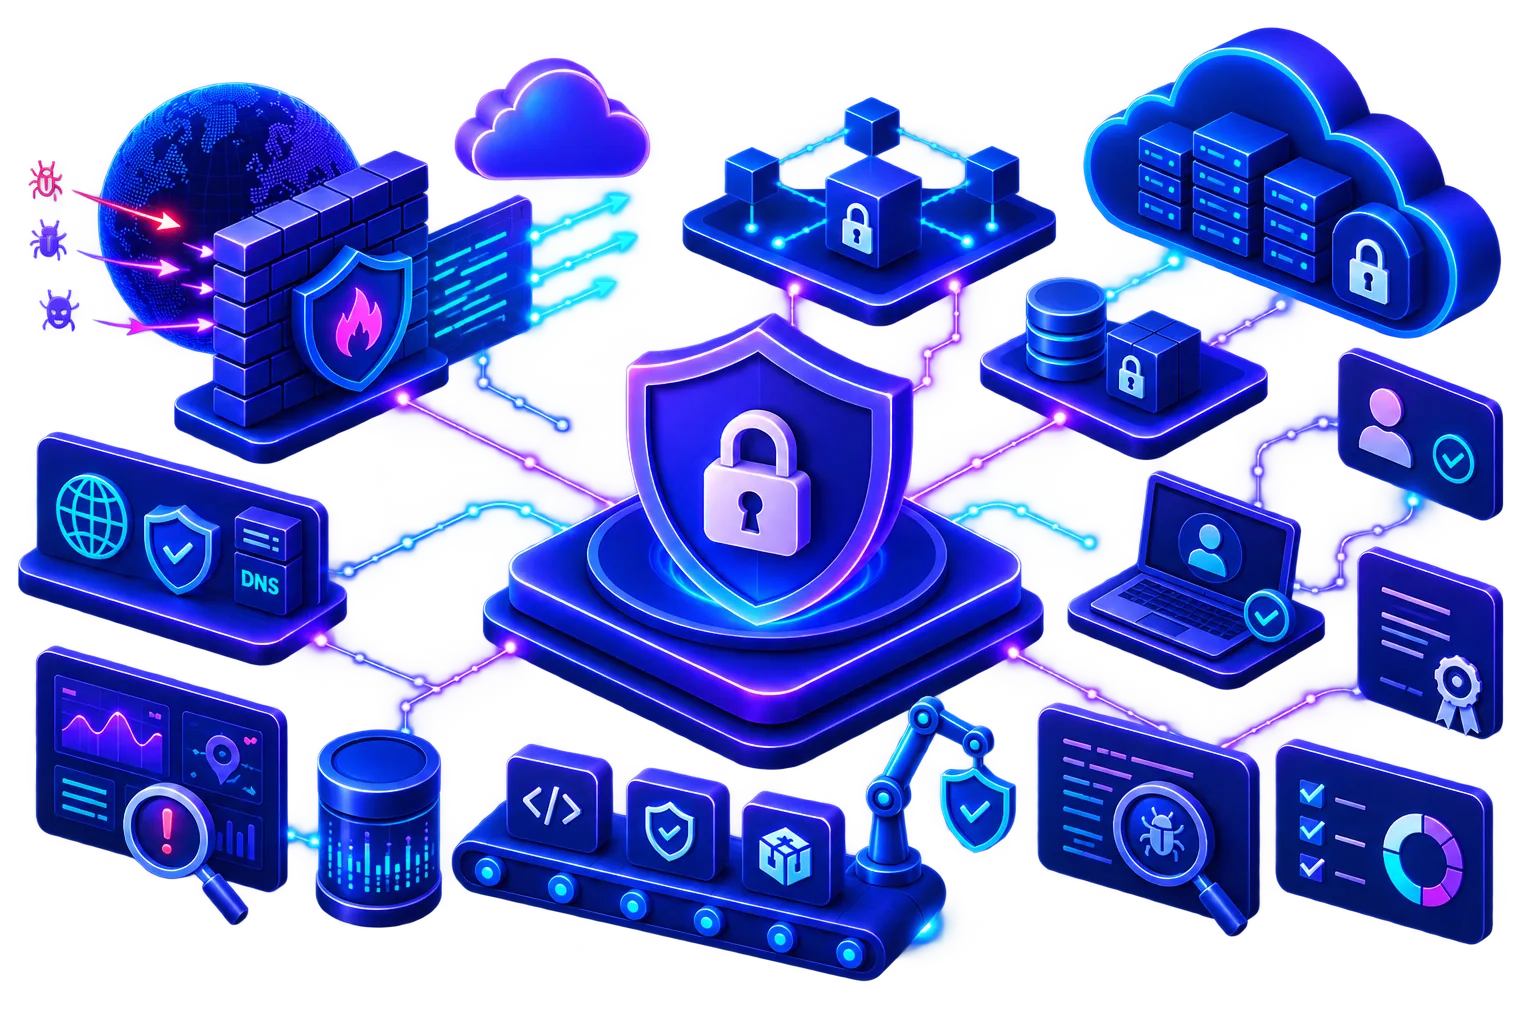
Security engineered into every layer - from edge to workload to pipeline.
What this delivers
Security is most effective when it is designed into the systems teams use every day. We connect threat-informed controls across the edge, network, workload and delivery pipeline, making protection practical to operate rather than a separate compliance exercise.
Controls are paired with evidence, telemetry and clear response paths. Teams can ship with confidence while security and risk stakeholders gain visibility into the posture, exceptions and remediation work that matter most.
Security Engineering Services
From strategy and architecture through to implementation and ongoing operation, we help you build the capabilities needed to deliver secure, reliable digital services. Engage us for consultancy and design, a complete project deliverable, embedded expertise alongside your team, or as your managed service provider.
Edge Security
Protect public entry points with deliberate controls for traffic, identity and abuse.
We assess how requests reach your services and apply layered controls that reduce exposure without impairing legitimate users.
Rules, monitoring and response procedures are designed as an operating capability rather than a one-time configuration.
What we deliver
- WAF, bot management and rate-limiting design
- DDoS and abuse-resilience controls
- TLS, certificate and security-header policy
- Edge logging and incident response signals
- Cloudflare and Azure Front Door specialist support
- Cloudflare
- Azure Front Door
Network Security
Network boundaries and connectivity controls aligned to workloads, identity and operational needs.
We make trust boundaries, data paths and privileged access explicit across cloud and hybrid estates.
The resulting network design is documented, testable and paired with detection signals that support ongoing assurance.
What we deliver
- Segmentation and workload connectivity design
- Private endpoints, egress and DNS controls
- Identity-aware administrative access
- Network telemetry, detection and review workflows
- Network design across Azure, AWS, and Google Cloud
- Azure
- AWS
- GCP
DevSecOps
Security controls integrated into delivery flows so safe change is also the efficient path.
We embed policy, secret handling and supply-chain controls into the pipelines teams already use.
Controls provide actionable feedback and evidence without turning delivery into a queue of manual approvals.
What we deliver
- Pipeline security and policy-as-code gates
- Secrets management and workload identity
- SBOM, provenance and artefact-signing practices
- Exception handling and audit evidence
- Snyk and Aqua Security integration for developer-focused security feedback
- Kyverno and Gatekeeper admission control for Kubernetes policy enforcement
- Azure Policy integration and management for cloud governance
- Snyk
- AquaSec
- SonarQube
- Kyverno
- OPA Gatekeeper
SAST & DAST
Application security testing that produces prioritised remediation rather than unmanaged finding volumes.
We integrate code and runtime testing where it is useful, calibrating tools to application risk and developer workflows.
Findings are triaged with ownership and remediation routes so security signals lead to measurable reduction in exposure.
What we deliver
- SAST and dependency scanning integration
- DAST design for representative runtime paths
- Finding triage, severity calibration and ownership
- Remediation metrics and recurring assurance reviews
- Registry, repository, cluster, and cloud infrastructure scanning with Snyk and Aqua Security
- Snyk
- AquaSec
Need help with security engineering?
Tell us where you are today and we'll come back with a candid view of what would actually move the needle.